

Writing a privacy policy for your app sounds simple until you sit down to do it. You open a blank page, have no idea what the document is supposed to say, and end up copying someone else's policy that describes data your app never touches. A privacy policy generator solves that by asking a few plain questions about your app and assembling the answers into a structured draft you can copy in minutes. The generator on this site works that way and runs entirely in your browser with nothing uploaded to a server, and never asks you to register.
Before we go further, let's be honest about what you're getting. The tool produces a starting point that you have to read, edit, and match to what your app actually does. It is not legal advice, and generating a document does not make you compliant with any specific law. With that understood, here is why your app needs a policy, what it has to cover, and how to produce one quickly.
Why your app needs a privacy policy
The most concrete reason is that the app stores require one. Apple's review guideline 5.1.1 requires every app to link its policy in App Store Connect and inside the app. Google's Prepare your app for review page requires the link on the store listing and in the app for apps that handle data covered by its User Data policy, which in practice means almost any app with analytics, ads or sign-in. A missing or broken link is a common reason a submission gets held up.
The second reason is trust. A clear policy tells users what your app collects and why, in language they can actually read. When someone is deciding whether to grant location access or hand over their email, a plain-spoken policy is the difference between a permission prompt that feels reasonable and one that feels like a red flag.
What a privacy policy must cover
A usable policy doesn't need to be long, but it must answer a handful of questions clearly:
- The data you collect. Email, name, device identifiers, location, usage analytics — whatever applies. List what your app actually touches, not a generic catch-all.
- Why you collect it. Each type of data should have a purpose: authentication, support, crash reporting, personalization, and so on.
- Third parties and SDKs. If your app sends data to outside services — an analytics provider, an ad network, push notifications — name them. SDKs like Firebase or AdMob count here, and only you know which ones are in your build.
- How to contact you. Users and the stores expect a way to reach you with privacy questions, usually an email address.
The structure is the easy part; accuracy is the judgment call. The document has to mirror what your app really does, because a policy that contradicts your actual behavior is worse than none.
What a finished policy for a real app looks like
Before generating anything, it helps to see the target. This is the section list of the policy I publish for Media Rescue, one of my own Android apps, at nasrtech.dev/mediarescue/privacy.html:
- Your photos never leave your phone: what the app does with files, and the statement that nothing is uploaded or stored on a server.
- Folder access: which folders the app asks for, through Android's own folder picker, and how to take access away.
- Memory cards are only read: a statement about the USB reader permission and that the app never writes to a card.
- What we collect: the two Google SDKs in the build, Firebase Analytics and Firebase Crashlytics, what each one records, and that there are no ads and no advertising ID.
- Permissions we use, one line per permission with the reason.
- Purchases, Children, Your choices and your rights, Changes to this policy and Contact.
Notice what is not there: no clause about location, contacts or accounts, because the app has none of them. A policy is only as good as its match with the build. That is the standard to hold a generated draft to.
How to generate one
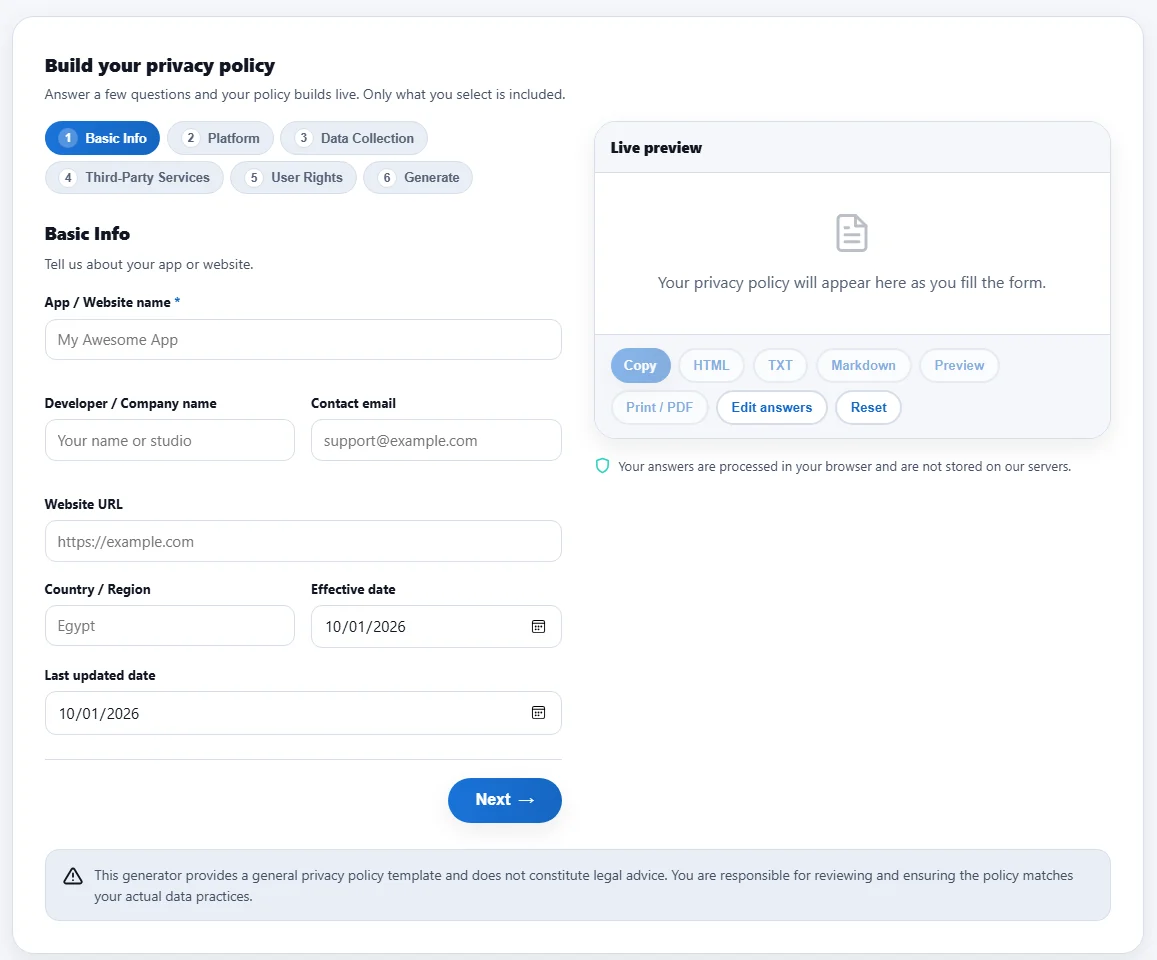
Producing a draft takes three steps with the privacy policy generator.
- Enter your basics. Add your app or site name and the contact details you want users to see.
- Select the data you actually collect. Don't tick a box just because it's common — choose the items that genuinely match your app, and add the third-party services you really use.
- Copy the result and review it line by line. Edit anything that doesn't apply, delete what isn't yours, then publish it at a stable URL the stores and your users can reach.
Everything happens locally in your browser. Your answers are not sent anywhere and nothing is stored on our side, so when you close the tab no trace is left behind. That makes the privacy policy generator private, fast, and completely free — and it keeps working offline once the page has loaded.
Connecting it to Google Play Data Safety
Google Play adds a wrinkle beyond the URL: the Data safety section. Inside the Play Console you declare exactly what data your app collects and shares, and the critical rule is that your published policy and that declaration have to agree — any contradiction can get your app rejected or pulled. If you are targeting Android, the Google Play privacy policy generator helps you produce a policy with that alignment in mind, so the document you link matches what you declare. The App Store has a parallel mechanism in its App Privacy "nutrition labels," and the same principle holds: what you write must describe what you actually do.
A note on legal advice
To be plain: this tool gives you a structured draft, not a legal opinion. It does not guarantee compliance with the GDPR, the CCPA, or any local regulation — that depends on your real data practices and your review of the text, not on the act of generating it. And it can't know what your app collects; you are the only source of truth, so inaccurate input produces an inaccurate policy. If your app handles sensitive categories — children's data, health, or financial information — treat the draft as a first pass and consult a qualified professional before you publish.
Two things people ask
Is this enough to get the app approved on Google Play? Google Play requires both a privacy policy URL and a completed Data safety section. The tool helps you produce the URL. Approval depends on the policy matching what you declare and what the app actually does, and that part is yours.
Turning a website into an app? With a paid plan, our website to app builder hosts a privacy page for the app it builds, so you have a fixed URL ready for Play Console.
What do I write about Firebase or AdMob? Mention them only if the app actually uses them. The tool cannot see inside your build, so it will include whatever you tick: do not add a service you do not use, and do not leave out one you do. Each SDK vendor documents what it collects; Google's own services publish Data safety guidance for exactly this purpose.